ISO 27002, the implementation guidance behind every Annex A control.
27001 names the controls. 27002 tells you how to build them - purpose, guidance, and context for all 93. Cybereen embeds the 27002:2022 text against every control, so the "how" is one click from the "what".
The "how" - not the "whether".
ISO/IEC 27002:2022 is the code of practice for information security controls. Where ISO 27001 Annex A lists each control as a single line, 27002 gives it a purpose, detailed implementation guidance, and supporting context.
You don't certify against 27002 - it isn't an auditable management system. You implement with it. It's the reference your engineers, HR leads, and facilities team actually read when they build a control, and the source your Statement of Applicability justifications lean on.
The 2022 revision was a structural reset: 114 controls collapsed into 93, regrouped from 14 domains into four themes, with 11 new controls reflecting cloud, privacy, and modern threats - plus a new five-attribute taxonomy so you can slice the catalogue by control type, CIA property, or cybersecurity concept.
Every 27002 entry, in four parts. Cybereen keeps all four together.
2022 gave each control a consistent layout. Read it once and every control reads the same way - and so does Cybereen's control detail view.
What to put in place.
The control statement itself - the measure you implement. The same wording you'll cite in your Annex A Statement of Applicability.
- One-line control text
- Maps to a 27001 Annex A ref
- Include / exclude decision
Why it exists.
The risk or objective the control addresses - the sentence your auditor wants when they ask "why is this applicable?".
- Risk it mitigates
- SoA justification source
- Plain-English rationale
How to implement it.
The detailed "how" - the bulk of 27002. Step-by-step implementation advice your team works from, not a one-liner.
- Implementation detail
- Policy + config pointers
- What evidence to keep
How to slice it.
Five tags per control - type, CIA property, cyber concept, operational capability, security domain - so you can build filtered views and cross-walks.
- Preventive / detective / corrective
- Maps to NIST CSF functions
- Filterable in Cybereen
93 controls. Four themes. Guidance on every one.
27002 shares 27001's four-theme structure exactly - so the guidance lines up one-to-one with your Annex A. Cybereen carries the 27002 text against each control, with its purpose and attributes.
Policies, roles, supplier and cloud security, threat intelligence, asset management. The "who-decides-what" layer - and the largest theme.
Screening, terms of employment, awareness, remote working, disciplinary process. Pre-, during-, and post-employment.
Secure areas, equipment, physical-security monitoring, clear desk/screen, supporting utilities. The doors, locks, and cameras.
Access management, cryptography, secure development, network security, logging, data masking, DLP, web filtering. The deepest theme.
Collect and analyse threat information systematically, and feed it into your risk reviews.
Acquire, use, and exit cloud services securely - shared-responsibility and exit plans documented.
Mask, pseudonymise, or anonymise data to limit exposure - especially in non-production environments.
Build-time guardrails - code review, SAST, dependency hygiene - evidenced from your CI pipeline.
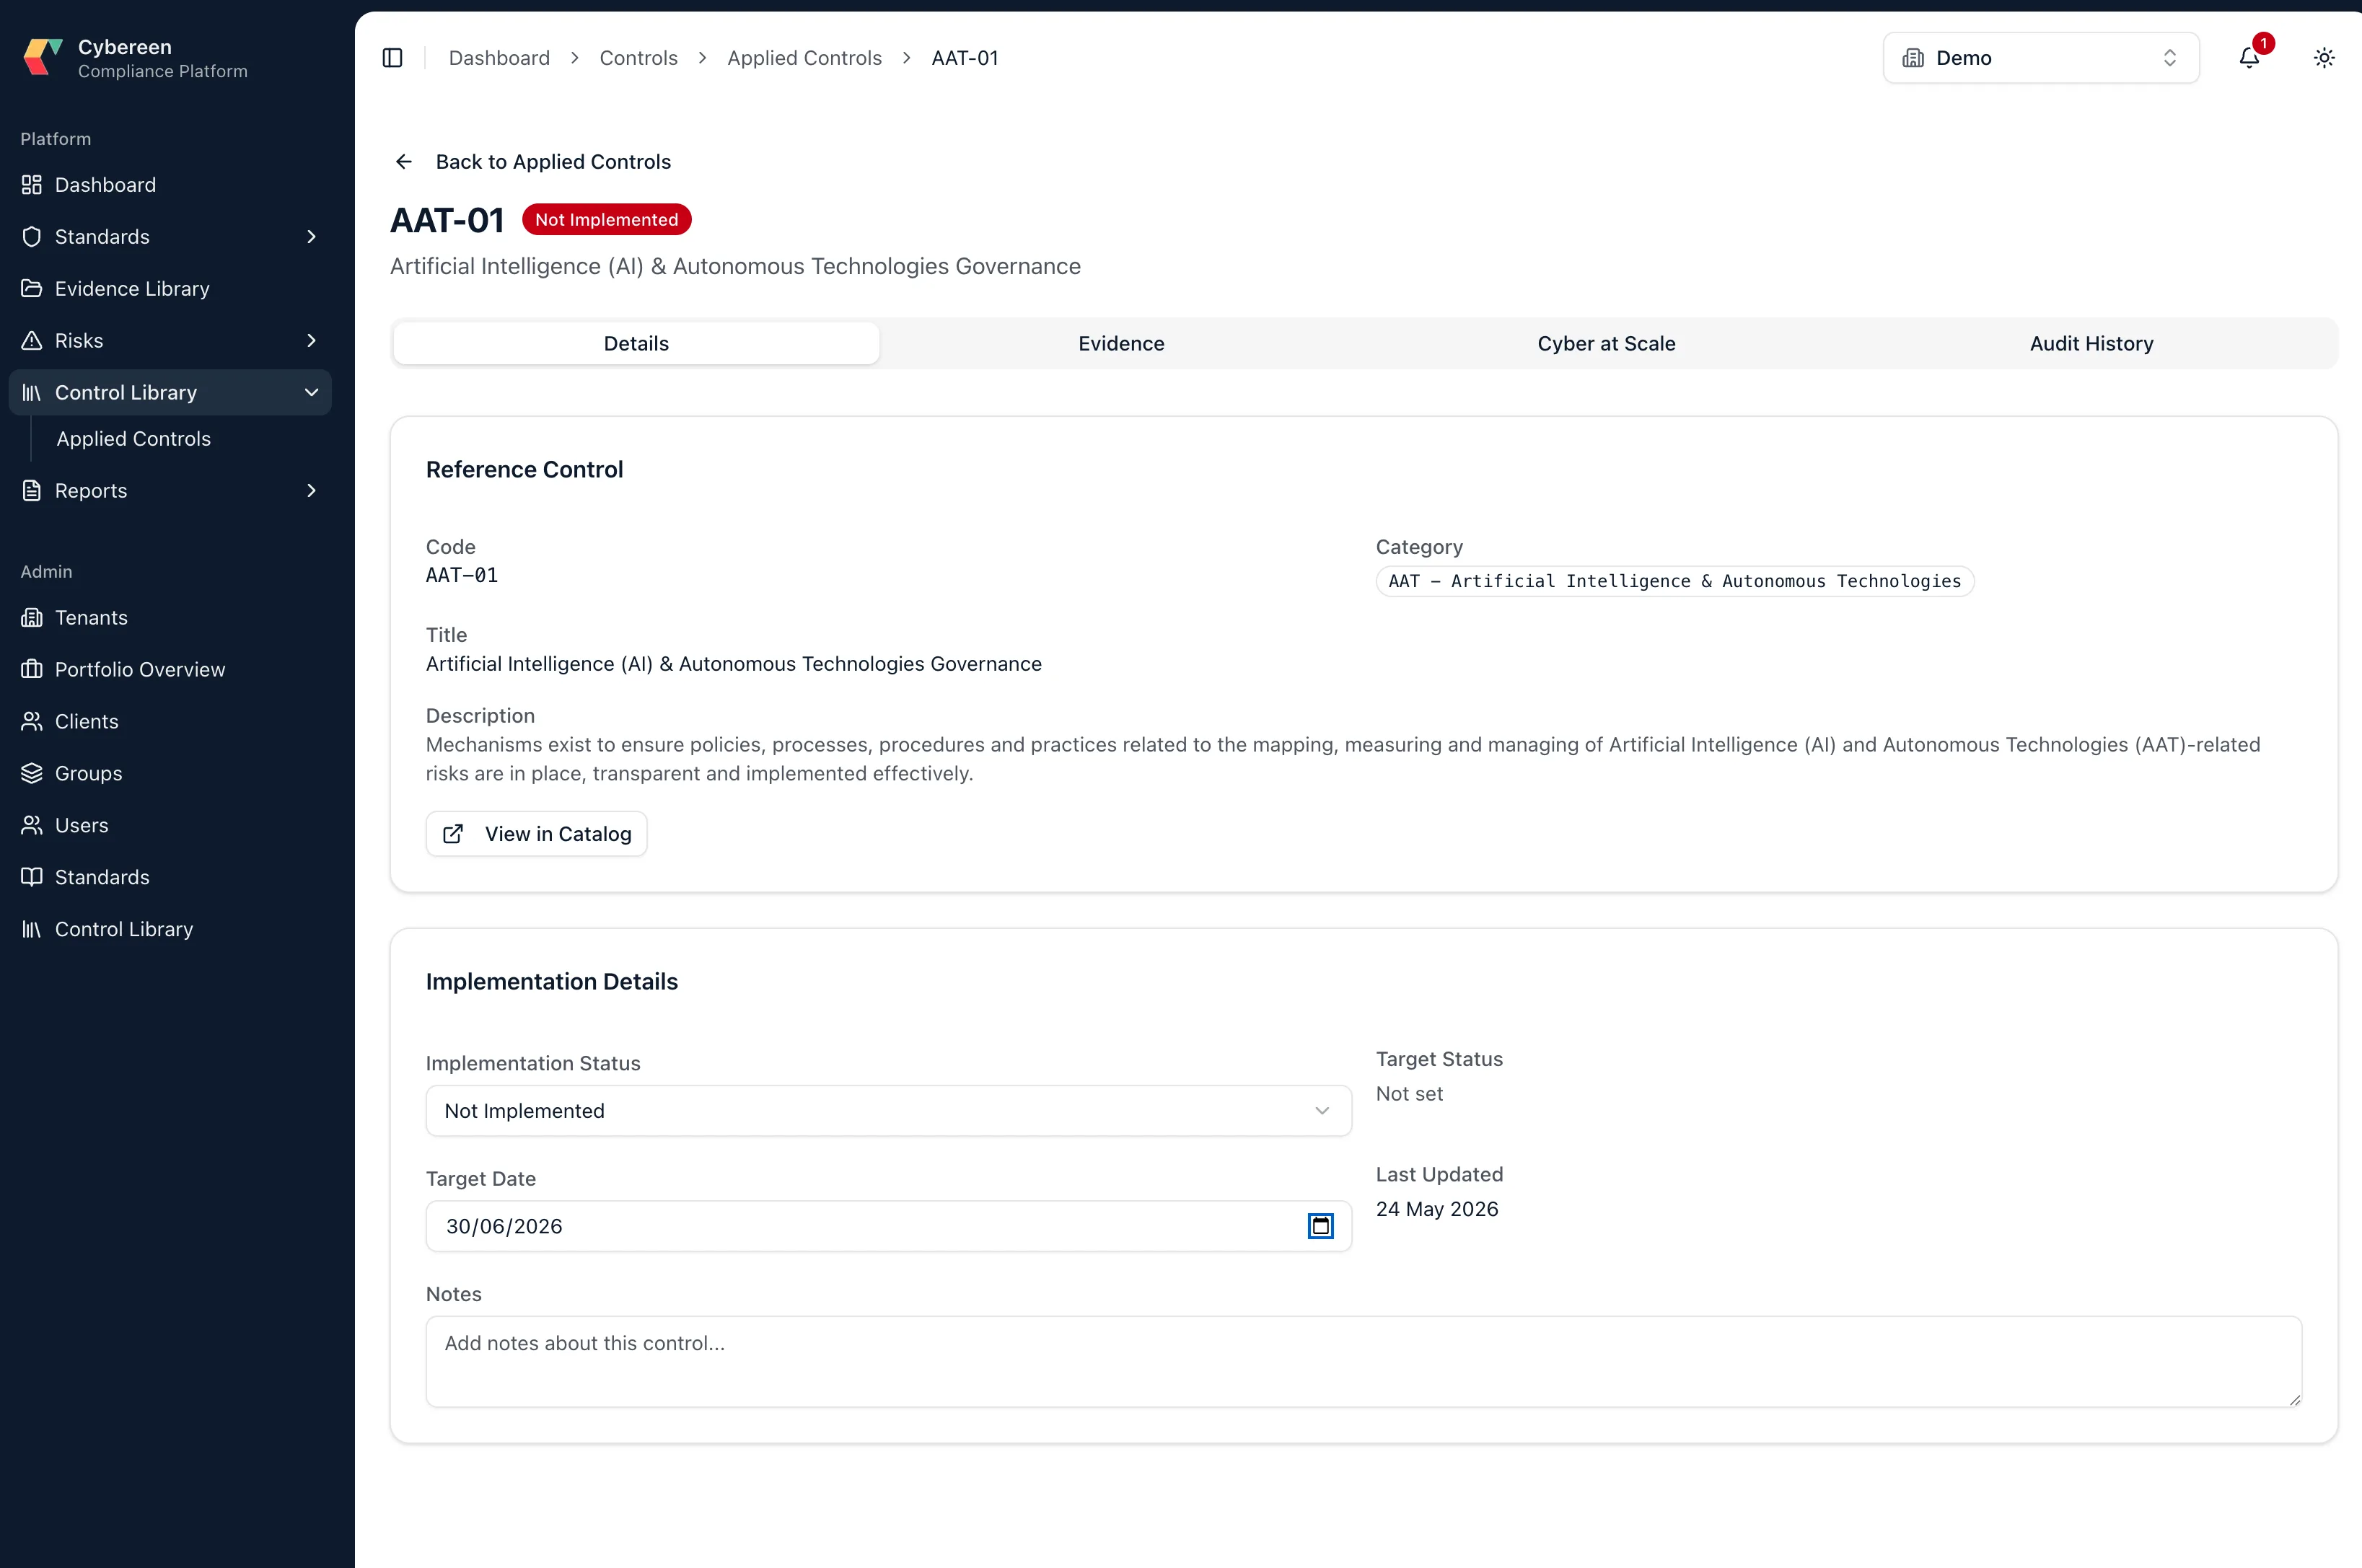
Guidance, inline. Against every control.
Open any Annex A control and the 27002:2022 purpose and guidance are right there - no second tab, no out-of-date PDF. Your SoA justification writes itself from the purpose text.
- Guidance text embedded - the 27002 "how" sits against the matching 27001 control.
- Purpose → SoA - the control's purpose pre-fills your Statement of Applicability justification.
- Five-attribute filters - slice the catalogue by control type, CIA, or cyber concept.
- 2013 → 2022 mapping - see merged, retired, and new controls side by side.
- One source of truth - update guidance once; every framework that reuses the control sees it.
Three ways teams misuse 27002.
Patterns Cybereen sees when 27002 is treated as a document instead of a working reference.
Trying to "certify against 27002".
You can't. 27002 is guidance, not a management system - there's no certificate. You certify against 27001 and implement with 27002. Procurement teams that ask for an "ISO 27002 certificate" mean 27001.
Pasting guidance into policy verbatim.
27002's text is generic by design. Copying it word-for-word produces policies that don't match how your organisation actually works - and auditors notice immediately.
Ignoring the 2022 attributes.
The five attributes aren't decoration - they're how you build cross-walks to NIST CSF, prioritise by control type, and report by security domain. Skipping them means rebuilding those views by hand.
27002 vs 27001, and what changed in 2022.
If yours isn't here, the contact form has a free-text field - answers go in the next page revision.
What is ISO 27002?
What's the difference between ISO 27001 and 27002?
Do we need both?
What changed in the 2022 revision?
What are the five attributes for?
How does Cybereen use 27002?
See the 27002 guidance against your own controls.
Open a control, read the purpose and guidance, generate the SoA line - without a 150-page PDF on the side. Book a walk-through and we'll show you on your frameworks.